
Saarth Infosec Private Limited is a Pune-based information security firm that helps businesses strengthen their cyber posture and meet regulatory or client-driven security requirements. Saarth Infosec provide end-to-end cybersecurity services to businesses across Ravet, Pune, and PCMC, from VAPT and phishing protection to ISO 27001, DPDPA compliance, and Virtual CISO support. They help keep your business protected.
The team works with organizations that are serious about protecting what they’ve built. Whether it’s customer data, internal systems, user-facing applications, or day-to-day digital operations, Saarth Infosec helps businesses understand where they’re exposed and what to do about it without the jargon overload.
Ransomware | Vendor Risks | Phishing | Cyber Insurance | Cloud Security | Insider Threats | AI Scams
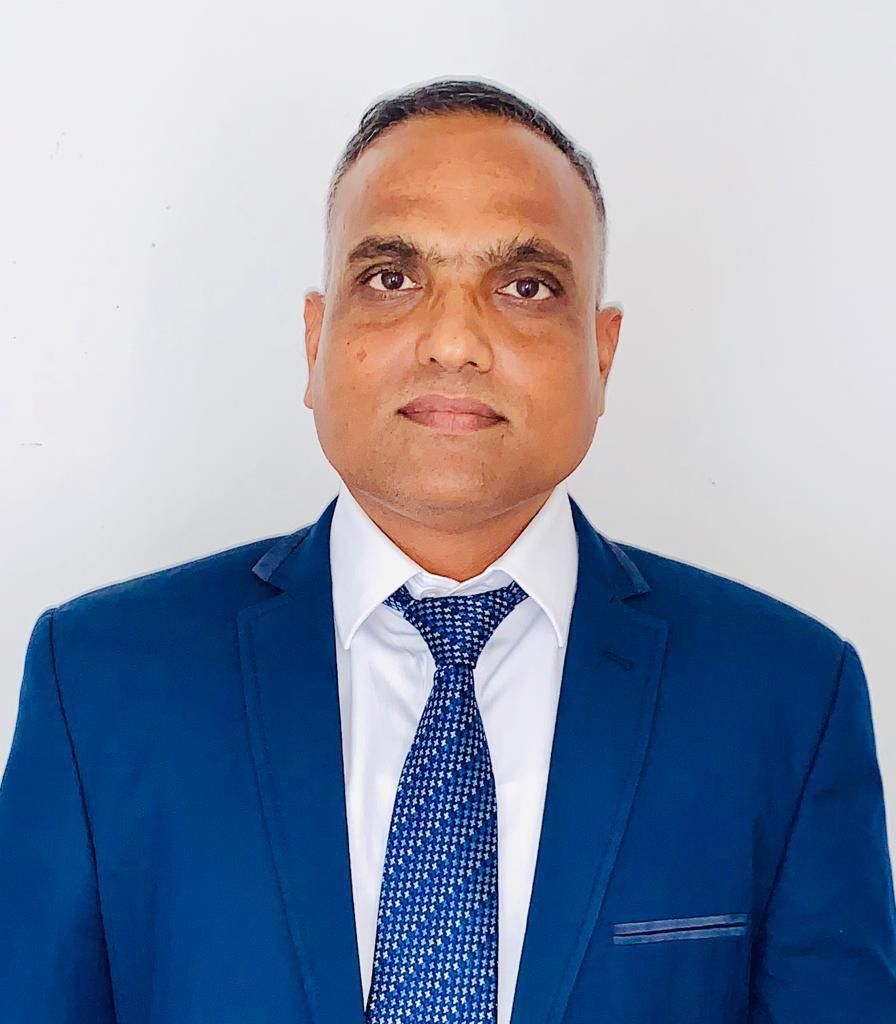
Mohan Jadhav
Director & CISO
➤ Director & CISO at Saarth Infosec Private Limited
➤ Certified and practicing CISO
➤ 20+ years of multi-national experience
➤ Expertise in cyber security leadership
➤ Strong background in information security governance
➤ Certified in C/CISO, DPO, CISM, PMP, DCPP, DCPLA, ITIL and CCNA
➤ Helps organizations build stronger cyber resilience
➤ Skilled in enterprise risk management
Why Businesses in Ravet, Need Cyber Security Services
Most businesses in Ravet think antivirus and firewalls are enough and that’s exactly what attackers count on. The real risks often hide in weak passwords, unchecked access, untested websites, and a single phishing email that slips through. A professional security assessment finds these gaps before someone else does. As more of these businesses run on digital systems, the exposure to cyber risk has grown quietly alongside them. Attacks today don’t discriminate by size and a single breach, audit failure or data leak can cost far more than prevention ever would.
Common risks businesses face:
- Weak website and application security
- Unpatched systems and outdated software
- Poor password and access control practices
- No formal cyber security policies in place
- Insecure cloud storage and file sharing
- Phishing and email-based fraud
- Ransomware exposure
- Unchecked vendor and third-party access
- No incident response plan
- Absence of data privacy compliance processes
- Missing audit-ready documentation
- Unclear security ownership within the team
Saarth Infosec helps businesses across Ravet and nearby areas tackle these risks with a structured, practical and measurable approach before a problem forces their hand.
Which Businesses in Ravet Need Cyber Security Services?
Every business handles data and every business is a target. Whether you’re a hospital safeguarding patient records, a startup building your first security policy, or a manufacturer managing vendor risks, Saarth Infosec has a solution tailored for you.
| Business Type | Recommended Service |
|---|---|
| IT Companies | VAPT, cloud security, application security |
| Clinics & Hospitals | DPDPA compliance, data protection consulting |
| Schools & Institutes | Phishing awareness, access control review |
| Manufacturers | Risk assessment, vendor security, ISO 27001 |
| Startups | Virtual CISO, policy setup, compliance roadmap |
| E-commerce Businesses | Website security testing, payment risk review |
Cyber Security Company in Ravet Pune
Services Offered by Saarth Infosec in Ravet, Pune
1. Cyber Security Consulting in Ravet, Pune
At Saarth Infosec, we understand that navigating the world of cyber security can feel overwhelming especially when you’re trying to run a business at the same time. That’s why our cyber security consulting service is designed to give you the expert guidance you actually need, without the jargon overload.
Whether you’re just starting to think about security or looking to strengthen what you already have, we work alongside your team to get a clear picture of where you stand and what needs to change.
Here’s what that looks like in practice:
1. Security gap assessment — We take a close look at your current setup to spot the gaps before someone else does
2. Risk identification — Not all risks are equal. We help you understand which ones actually matter for your business.
3. Cyber security roadmap planning — No overnight overhauls. We build a practical, step-by-step plan that fits your pace and budget.
4. Review of existing IT controls — We assess what’s already in place and whether it’s doing the job it should.
5. Security policy guidance — Clear, usable policies your team will actually follow not ones that gather dust in a folder.
6. Employee awareness planning — Your people are your first line of defense. We help you keep them informed and alert.
7. Incident readiness support — Because it’s not just about prevention it’s about knowing what to do when something goes wrong.
8. Compliance preparation — We help you get audit-ready without the last-minute scramble.
9. Vendor risk review — Your security is only as strong as the partners you work with. We help you vet them properly.
10. Security maturity improvement — Wherever you are today, we help you build toward a stronger, more resilient tomorrow.
Cyber Security Company in Ravet Pune
2. Information Security Consulting in Ravet, Pune
Business information is everywhere sitting in your systems, moving through emails, stored across databases, living on employee devices, spread across cloud platforms, and shared with vendors. And every single one of those touchpoints is a potential vulnerability.
At Saarth Infosec, we help businesses bring order to all of that. Our information security consulting is about building a structure that actually holds one where your data is protected not just in theory, but in the day-to-day reality of how your business operates.
We work with you to put the right foundations in place:
1. Information security policies — Practical, clear policies that set the ground rules for how information is handled across your organization.
2. Access control review — Making sure the right people have access to the right information and nobody else does.
3. Data handling guidelines — Simple, workable guidelines so your team knows exactly how to manage sensitive information responsibly.
4. Risk assessment support — Identifying where your information is most at risk, so you can focus your efforts where they matter most.
5. Security governance planning — Helping you build the oversight and accountability structures that keep security on track long-term.
6. Documentation support — Getting your security documentation in order thorough, accurate, and ready when you need it.
7. Audit preparation — So when an audit comes around, you’re walking in prepared not scrambling at the last minute.
8. Staff awareness — Helping your team understand their role in keeping information secure, because policies only work when people follow them.
9. Internal control improvement — Strengthening the controls already inside your organization to close gaps and reduce exposure.
10. Data protection practices — Building habits and processes that protect sensitive data consistently, not just when someone’s watching.
Cyber Security Company in Ravet Pune
3. VAPT Services in Ravet, Pune
Every business has digital assets websites, applications, servers, networks, cloud systems. And somewhere within all of that, there are almost always weaknesses. The question isn’t whether vulnerabilities exist. It’s whether you find them first, or whether someone else does.
That’s exactly what VAPT — Vulnerability Assessment and Penetration Testing is designed to answer.
At Saarth Infosec, we don’t just run automated scans and hand you a report. We take a thorough, methodical approach to finding real weaknesses in your environment — the kind that actual attackers look for — so you can fix them before they become a problem.
Saarth Infosec provides VAPT services in Ravet Pune for:
1. Websites — Your public face online shouldn’t also be your biggest vulnerability.
2. Web applications — Complex apps carry complex risks. We dig deep into how they behave under pressure.
3. Mobile applications — Android or iOS, we test how your mobile apps hold up against real-world attack techniques.
4. APIs — Often overlooked, APIs are a common entry point for attackers. We make sure yours are locked down.
5. Servers — We assess your servers for misconfigurations, outdated software, and exploitable weaknesses.
6. Networks — Internal and external network testing to map out what an attacker could access and how.
7. Cloud environments — Cloud doesn’t mean secure by default. We review your cloud setup for gaps and misconfigurations.
8. IT infrastructure — A broad look at the systems that keep your business running and what could bring them down.
9. Firewalls and exposed systems — We check what’s visible from the outside and whether your defenses are actually holding the line.
Cyber Security Company in Ravet Pune
4. DPDPA Compliance Consultant in Ravet, Pune
If your business collects, stores, or processes personal data in any form customer details, employee records, user information data privacy is no longer something you can put off for later. With India’s Digital Personal Data Protection Act now in the picture, organizations need to take a honest look at how they handle personal data and whether their current practices actually measure up.
At Saarth Infosec, we help businesses in Ravet and across Pune make sense of DPDPA compliance not just ticking boxes, but genuinely building privacy practices that protect people and reduce your organization’s risk.
We understand that compliance can feel like a maze, especially when you’re trying to run a business at the same time. That’s why our approach is practical, straightforward, and built around your specific situation.
DPDPA Compliance Support Covers
1. Personal data mapping — Before you can protect your data, you need to know where it lives. We help you trace exactly what personal data your organization collects, where it goes, and who handles it.
2. Privacy gap assessment — An honest look at where your current practices fall short of DPDPA requirements so you know what needs attention and where to focus first.
3.Consent process review — Checking whether the way you collect consent from individuals is valid, clear, and compliant with what the law actually requires.
4. Privacy notice review — Your privacy notices should be transparent and easy to understand. We review them to make sure they say what they need to —and mean what they say.
5. Data retention guidance — Helping you establish clear rules around how long personal data is kept and when it should be deleted because holding on to data longer than necessary is a risk in itself.
6. Vendor and processor review — If you share personal data with third parties, their practices matter too. We help you assess the privacy risks in your vendor relationships.
7. Internal privacy controls — Building the internal processes and safeguards that keep personal data protected day to day, not just on paper.
8. Employee awareness — Your team handles personal data constantly, often without realizing the implications. We help them understand their responsibilities in plain, relatable terms.
9. Documentation support — Getting your privacy documentation in order policies, records, notices so you’re not caught unprepared when it matters most.
10. Compliance roadmap planning — A realistic, step-by-step plan to move your organization toward DPDPA compliance without disrupting how your business operates.
Cyber Security Services in Ravet Pune
5. GRC Consulting in Ravet, Pune
Running a business means making hundreds of decisions every day. But when it comes to cyber security, risk, and compliance — how confident are you that those decisions are being made in a structured, accountable way? Are the right people responsible for the right things? Are your risks being tracked? Are you staying on top of what regulations and standards require of you?
That’s where GRC comes in.
Governance, Risk and Compliance isn’t just a framework — it’s the backbone of a security program that actually holds together under pressure. At Saarth Infosec, we help businesses in Ravet and across Pune build that backbone — bringing clarity, structure, and accountability to the way they manage cyber security decisions, handle risk, and meet compliance obligations.
Whether you’re building your GRC program from scratch or trying to bring more order to what already exists, we work with you to make it practical, not just theoretical.
GRC Consulting Covers
- Risk register creation — Giving your organization a clear, maintained view of the risks it faces what they are, how serious they are, and what’s being done about them. No more risks living only in someone’s head.
- Policy framework development — Building a set of security policies that are coherent, consistent, and actually usable policies that guide behavior rather than sit unread in a shared drive.
- Control mapping — Connecting your security controls to the frameworks, regulations, and standards that matter to your business, so nothing falls through the cracks.
- Compliance tracking — Keeping a structured eye on your compliance obligations so you always know where you stand and what still needs attention.
- Internal audit support — Helping you prepare for and navigate internal audits with confidence, turning what can feel like a stressful process into a straightforward one.
- Management review preparation — Making sure your leadership has the right information, in the right format, to make informed decisions about security and risk at the top level.
- Corrective action planning — When gaps or issues are identified, we help you build a realistic, trackable plan to address them not just acknowledge them.
- Vendor risk governance — Extending your risk management approach to the third parties your business depends on, because your governance is only as strong as the weakest link in your supply chain.
- Security responsibility mapping — Defining clearly who owns what when it comes to security so accountability is real, not just assumed.
- Documentation improvement — Strengthening the quality and completeness of your GRC documentation, making sure it reflects what’s actually happening in your organization and stands up to scrutiny.
6. ISO 27001 Consultant in Ravet, Pune
As a recognized standard for information security management, ISO 27001 tells the world your clients, your partners, your regulators that your organization takes security seriously and has the systems in place to prove it. For IT companies, SaaS businesses, service providers, and B2B organizations especially, it’s fast becoming less of a nice-to-have and more of an expectation.
At Saarth Infosec, we help businesses in Ravet and across Pune navigate the journey to ISO 27001 certification from the very first gap assessment all the way through to audit readiness. We’ve seen how overwhelming the process can feel at the start, and we’re here to make it structured, manageable, and genuinely useful not just a paper exercise.
ISO 27001 Consulting Covers
- ISMS gap assessment — We start by understanding where you are today. A clear, honest assessment of how your current practices compare to what ISO 27001 requires so you know exactly what the journey ahead looks like.
- Scope definition — Defining the right boundaries for your Information Security Management System is critical. We help you determine what should be included and why, in a way that’s practical and defensible.
- Risk assessment — A thorough, structured look at the information security risks your organization faces identifying them, understanding their impact, and laying the groundwork for how to treat them.
- Risk assessment — A thorough, structured look at the information security risks your organization faces identifying them, understanding their impact, and laying the groundwork for how to treat them.
- Risk treatment planning — Turning risk assessment findings into a concrete plan of action deciding which risks to address, how to address them, and in what order.
- Security policy documentation — Developing the policies your ISMS needs clear, relevant, and written in a way that your team can actually understand and follow.
- Control implementation guidance — ISO 27001 requires a set of security controls. We guide you through selecting and implementing the ones that are right for your organization’s risk profile and scope.
- Statement of Applicability support — One of the most important documents in your ISO 27001 journey. We help you build a thorough, well-reasoned Statement of Applicability that holds up under scrutiny.
- Internal audit preparation — Helping you conduct meaningful internal audits that genuinely test your ISMS and prepare you for what external auditors will be looking at.
- Management review support — Making sure your leadership is engaged in the ISMS process in the way ISO 27001 requires with the right information, the right conversations, and proper documentation.
- Certification audit readiness — When it’s time for the certification audit, we make sure you’re walking in prepared with your documentation in order, your controls in place, and your team ready to demonstrate what you’ve built.
7. IT Security Consulting in Ravet, Pune
Most cyber attacks don’t happen because of sophisticated, Hollywood-style hacking. They happen because of misconfigurations, outdated software, weak access controls, and security gaps that built up quietly over time often in systems that people assumed were fine.
IT security consulting is about taking an honest, technical look at your infrastructure, systems, and day-to-day operations and finding those gaps before someone else does.
At Saarth Infosec, we work with businesses in Ravet and across Pune to strengthen the technical foundations of their security. Not with generic recommendations pulled from a checklist, but with practical, specific guidance based on how your environment actually looks and operates.
IT Security Consulting Covers
- Network security review — Taking a close look at how your network is structured, what’s exposed, and where the weaknesses are that could let an attacker move through your environment unchallenged.
- Firewall configuration review — A firewall is only as good as its configuration. We review yours to make sure the rules are tight, current, and actually doing what they’re supposed to do.
- Endpoint security guidance — Laptops, desktops, mobile devices every endpoint is a potential entry point. We help you make sure they’re protected consistently, not just on paper.
- Server hardening — Servers often carry more risk than people realize, especially when they’re running with default settings or outdated configurations. We help you lock them down properly.
- Email security improvement — Email remains one of the most common ways attackers get in. We review your email security setup and help you reduce the risk of phishing, spoofing, and malicious attachments getting through.
- Backup and recovery review — Having backups isn’t enough if they’re not working correctly or can’t be restored when you need them. We assess whether your backup and recovery setup would actually hold up in a crisis.
- Backup and recovery review — Having backups isn’t enough if they’re not working correctly or can’t be restored when you need them. We assess whether your backup and recovery setup would actually hold up in a crisis.
- Patch management advisory — Unpatched systems are an open invitation. We help you build a patch management approach that keeps your environment up to date without disrupting operations.
- Cloud security review — Cloud environments come with their own set of risks misconfigurations, overly permissive access, exposed storage. We review your cloud setup and help you close the gaps.
- Remote access security — With more people working remotely, how your team connects to business systems matters enormously. We assess your remote access setup and make sure it’s not creating unnecessary exposure.
- User access control review — Who has access to what and do they actually need it? We review user access across your systems to reduce the risk of insider threats and compromised accounts causing serious damage.
- Security monitoring recommendations — You can’t respond to what you can’t see. We help you understand what monitoring capabilities you need and how to build visibility into your environment over time.
8. Data Privacy Consulting in Ravet, Pune
Think about how much personal information passes through your business on any given day. Customer details, employee records, patient information, financial data, contact lists it adds up quickly. And the people behind that data your customers, your clients, your staff are increasingly aware of their privacy rights and increasingly selective about which organizations they trust with their information.
Data privacy is no longer a back-office concern. It’s a business issue, a trust issue, and in the evolving Indian regulatory landscape, a compliance issue too.
- Privacy process review — We look at how personal data actually moves through your organization how it’s collected, who touches it, where it goes and identify where the risks and gaps are hiding.
- Data collection assessment — Are you collecting only what you genuinely need, or has data collection crept beyond what’s necessary? We help you step back and assess whether your collection practices are proportionate and justifiable.
- Data storage and retention review — Where is personal data being stored, how securely, and for how long? Holding onto data longer than necessary is a risk in itself we help you bring discipline to how long data stays and when it goes.
- Access control guidance — Personal data should only be accessible to people who genuinely need it. We assess who has access across your systems and help you tighten controls where they’re too loose.
- Privacy policy support — Your privacy policy is often the first thing people read to decide whether they trust you. We help you make sure it’s honest, clear, and actually reflects how your organization handles data not just legal boilerplate.
- Consent mechanism review — Collecting consent is one thing. Collecting it properly is another. We review whether your consent processes are valid, transparent, and giving individuals the genuine choice they’re entitled to.
- Third-party data sharing review — If personal data is being shared with vendors, partners, or service providers, their handling of that data reflects on you. We help you assess those relationships and make sure appropriate safeguards are in place.
- Privacy awareness support — Privacy practices only work when the people in your organization understand them. We help you build awareness across your team so that good data handling becomes part of how everyone works, not just a policy document somewhere.
- Data breach response planning — What would you do if personal data was compromised tomorrow? We help you build a clear, practical response plan so that if the worst happens, you’re not figuring it out under pressure.
Why Businesses Choose Saarth Infosec
At Saarth Infosec, we believe that good security advice shouldn’t feel like a lecture, and a security report shouldn’t require a decoder ring to understand. Everything we do is built around being clear, structured, and genuinely useful to the businesses we work with not just technically thorough.
Here’s what that looks like in practice:
1. Better understanding of cyber risks — We help you see your security landscape the way it actually is not through a fog of technical jargon, but with clarity about what risks exist, why they matter, and what they could mean for your business if left unaddressed.
2. Improved protection of sensitive data — Whether it’s customer information, employee records, or business-critical data, we help you put the right protections in place so that what matters most to your organization stays safe.
3. A clear security improvement roadmap — Security improvement doesn’t have to be chaotic or overwhelming. We give you a structured, prioritized path forward so you always know what you’re working toward and why.
4. Stronger application and network security — From your web applications to your internal networks, we help you identify and close the technical gaps that leave your environment exposed to attack.
5. Better compliance readiness — Whether it’s ISO 27001, DPDPA, or another framework your business needs to meet, we help you build toward compliance in a way that’s organized, trackable, and audit-ready.
6. Support for client security requirements — More and more, clients and enterprise customers want to know that their vendors take security seriously. We help you meet those expectations with credibility and confidence.
7. Improved internal policies and processes — Security only works when it’s embedded in how your organization operates day to day. We help you build the internal policies and processes that make that possible.
8. Better employee awareness — Your team is one of your greatest security assets or one of your biggest vulnerabilities, depending on how well they understand their role. We help you shift that balance in the right direction.
9. Reduced risk of business disruption — Cyber incidents don’t just compromise data they disrupt operations, damage reputation, and cost money. Stronger security means fewer disruptions and a more resilient business overall.
10. Professional VAPT reporting — Our vulnerability assessment and penetration testing reports are detailed, well-structured, and written to be useful giving your technical team what they need to act, and your leadership what they need to understand.
11. Professional VAPT reporting — Our vulnerability assessment and penetration testing reports are detailed, well-structured, and written to be useful giving your technical team what they need to act, and your leadership what they need to understand.
12. Access to Virtual CISO expertise — Not every business needs a full-time Chief Information Security Officer, but every business benefits from that level of thinking. Our Virtual CISO service gives you senior security leadership and strategic guidance without the overhead of a permanent hire.
13. Improved trust with clients and stakeholders — Ultimately, strong security is a signal. It tells your clients, your partners, and your stakeholders that you’re serious, responsible, and worth trusting with their business.
Client Testimonials
Saarth Infosec didn’t just hand us a report they actually walked us through what it all meant. Technical issues were explained in plain language, and we always knew what to prioritize. If you’re a business in Ravet looking for honest, practical security guidance, these are the people to call. – Rohan Kulkarni
We reached out to Saarth Infosec for VAPT and came away genuinely impressed. The report was thorough, the recommendations were actually actionable, and the team stayed professional and approachable throughout. Our internal team had no trouble picking up where they left off that’s rare. – Priya Deshmukh
Getting DPDPA-ready felt overwhelming until we worked with Saarth Infosec. They quickly spotted the gaps in our policies and laid out a clear, step-by-step plan that actually made sense for our team. For businesses around Ravet and PCMC looking for reliable compliance support, they’re a solid choice. – Neha Patil
Frequently Asked Questions About Cyber Security Company in Ravet Pune
1.What Is the Best Cyber Security Company in Ravet, Pune?
When it comes to protecting your business from cyber threats, choosing the right security partner can make all the difference between having genuine protection and simply having the appearance of it. For businesses in Ravet, Pune, Saarth Infosec Private Limited stands out as a reliable, experienced, and business-focused choice.
2. What Are VAPT Services and Why Are They Important?
VAPT — Vulnerability Assessment and Penetration Testing is essentially a controlled, expert attempt to find the weaknesses in your digital environment before a real attacker does. From websites and applications to APIs, servers, and networks, it uncovers the gaps that leave your business exposed. Saarth Infosec provides VAPT services in Ravet, Pune with clear, detailed reporting and practical remediation guidance so you don’t just know what’s broken you know exactly how to fix it.
3. Can Small Businesses in Ravet Afford Cyber Security Services?
Yes, and more importantly, small businesses can’t afford to ignore cyber security. Phishing attacks, ransomware, data leaks, and website vulnerabilities don’t discriminate by company size, and smaller businesses are often targeted precisely because their defenses tend to be lighter. Saarth Infosec works with small and mid-sized businesses in Ravet to find practical, right-sized solutions that fit their budget, their team, and their actual level of risk so strong security doesn’t have to mean overwhelming investment.
4. Is ISO 27001 Useful for Businesses in Ravet, Pune?
Yes, especially if your business handles sensitive data, works with enterprise clients, or operates in a space where security credibility matters. ISO 27001 gives you a formal, internationally recognized framework for managing information security, which tells clients and partners that your organization has done the work not just promised to. For businesses in Ravet and across Pune looking to improve trust, win better clients, and walk into audits with confidence, it’s one of the most valuable investments you can make.
5. What Is the Difference Between IT Security and Cyber Security?
Think of IT security as the foundation it’s focused on protecting your physical and digital infrastructure like networks, servers, devices, and software from threats of all kinds. Cyber security zooms out a little further, dealing specifically with protecting your digital assets and data from online threats, attacks, and breaches. At Saarth Infosec, we support businesses in Ravet and across Pune with both because in today’s environment, the line between the two matters far less than making sure neither is left unprotected.
Contact details
Address : Office- #136, VTP Trade Park, near Star Bazzar, Shree Siddhivinayak Meera, Undri, Pune, Maharashtra 411060
Phone no. : +91 8459122400 / +91 8390593233
Website : https://www.saarthinfosec.com/
Frequently Asked Questions
Cyber security consulting helps businesses identify digital risks, improve security controls, protect data, and create a clear plan to reduce cyber threats.
Businesses need cyber security services to protect websites, applications, customer data, internal systems, email accounts, and business operations from cyber attacks.
VAPT should ideally be done once a year or whenever there is a major change in the website, application, server, cloud setup, or IT infrastructure.
A Virtual CISO provides senior-level cyber security leadership without hiring a full-time CISO. It helps with strategy, risk management, policies, compliance, and security governance.
ISO 27001 consulting helps businesses implement an Information Security Management System to manage risks, protect data, and prepare for certification audits.
September, 2026
Thursday
-
12:00 pm - 12:30 pm
-
12:30 pm - 1:00 pm
-
1:00 pm - 1:30 pm
-
1:30 pm - 2:00 pm
-
2:00 pm - 2:30 pm
August 26,2019
- Tuesday
- 9:00am - 10:00am
Awesome Job!
We have received your appointment and will send you a confirmation to your provided email upon approval.
